Your Attack Surface
Your Attack Surface Is Bigger Than You Think: The Hidden Entry Points Hackers Look For
Your website might be secure. Your server might be patched. Your administrator password might be protected by two-factor authentication.
So you’re safe, right?
www.example.comYour website: HTTPS on every pageserverYour server: fully patched/adminYour admin login: two-factor on*.example.com6 more addresses nobody listed
Not necessarily.
Modern web applications are made up of far more than the website visitors see in their browsers. Behind every homepage are servers, databases, APIs, subdomains, development environments, third-party integrations, administrator interfaces and dozens of other components. Each one creates another potential entry point.
And here’s the problem: You might not even know some of them are accessible from the internet.
Hackers don’t necessarily attack the front door. Sometimes they find an old staging environment, an exposed database port, a forgotten subdomain or a development tool that was never supposed to be publicly accessible.
This is what cybersecurity professionals call your attack surface. Understanding exactly what is exposed, where it is exposed and how it could be exploited is one of the most important steps in protecting your application.
01Attack Surface
What Exactly Is An Attack Surface?
Your attack surface is the collection of all the points where someone could potentially interact with your systems, applications or infrastructure.
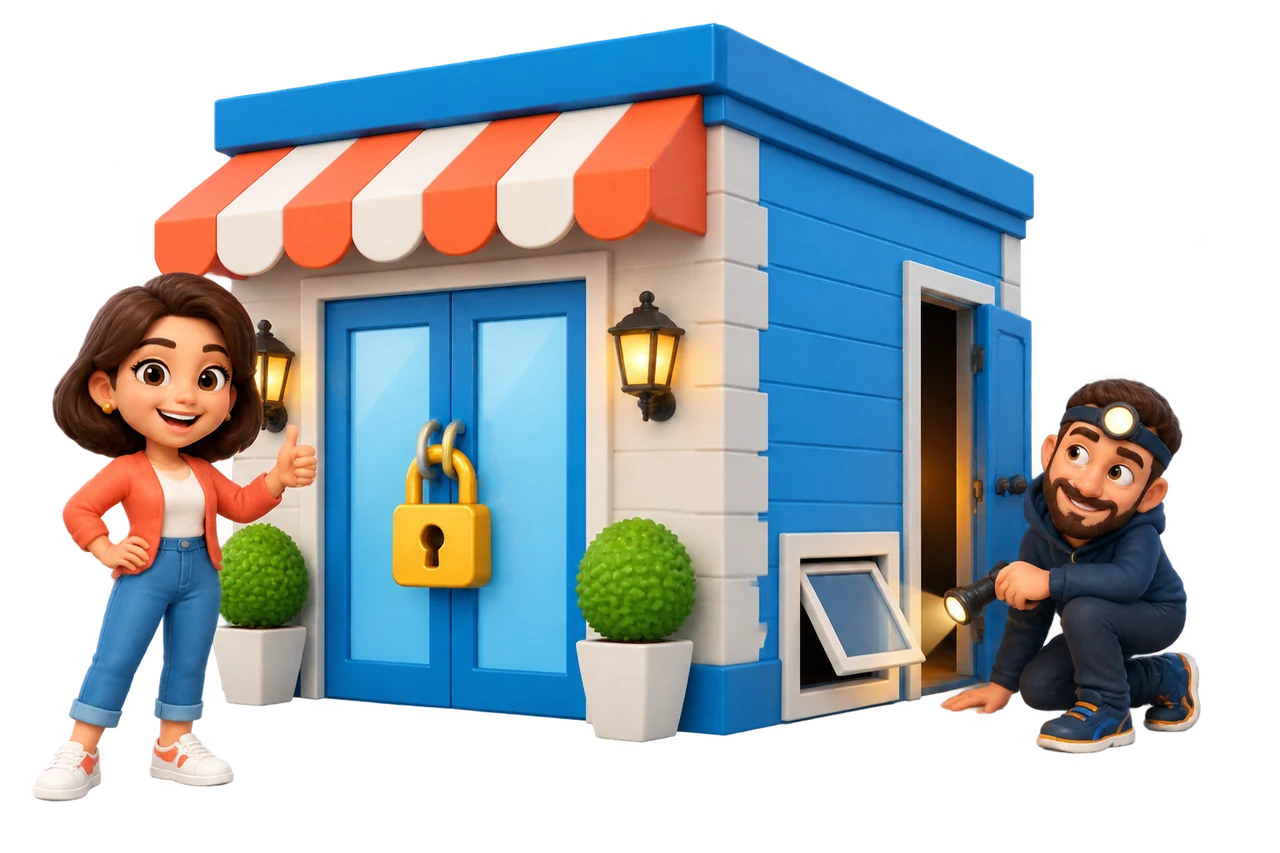
Think of your business as a building.
You might have a heavily secured front entrance, cameras, alarms and a sophisticated access control system. But what about the delivery entrance? The basement windows? The maintenance door that nobody remembers to lock?
Your digital infrastructure works in much the same way.
Every publicly accessible service, application endpoint, login interface and network connection represents another possible way into your environment. An attack surface typically includes:
Web Applications
Your website, customer portals, dashboards and administrative interfaces.
Servers And Infrastructure
VPS instances, hosting accounts, databases, SSH services and exposed network ports.
Domains And Subdomains
Production websites, staging environments, development systems and forgotten domains.
APIs
Endpoints used by your own front end, integrations, internal services and third-party platforms.
Third-Party Components
Plugins, frameworks, software packages and externally hosted services.
Development Environments
Testing servers, debugging tools, deployment systems and temporary applications.
The larger and more complicated your infrastructure becomes, the harder it can be to maintain a complete picture of everything that is exposed.
And that’s precisely where problems begin.
7 Hidden Entry Points That Could Expose Your Business
Some of the most interesting security problems aren’t found on the main website. They’re hiding in components that developers, administrators and business owners have simply forgotten about.
Here are seven areas we pay particular attention to when reviewing an application’s security.
02Subdomains
Forgotten Subdomains And Old Websites
Over time, businesses accumulate subdomains. You might start with three, and a year later there could be several more:
- www.example.com
- app.example.com
- admin.example.com
- staging.example.com
- dev.example.com
- beta.example.com
- old.example.com
- test.example.com
Some might belong to previous development projects. Others might have been created for temporary testing or an older version of the application.
The problem is that these environments don’t always receive the same attention as the production website.
An old application might still run outdated software, contain vulnerable plugins or use administrator credentials that haven’t been changed in years.
Even worse, a forgotten subdomain might point to infrastructure that is no longer maintained. If its DNS record still points at a hosting account or cloud service you have since closed, someone else can sometimes claim that service and publish their own content under your name. This is known as a subdomain takeover.1
03Open Ports
Exposed Database And Admin Ports
Your application needs to communicate with databases, caching systems, background services and other infrastructure.
However, these services don’t necessarily need to be accessible from the public internet. Consider a typical web application running on a VPS:
| Port | What It Is | Who Should Reach It |
|---|---|---|
| 22 | SSH administration | Your team, from known addresses |
| 80 | HTTP traffic | Everyone, redirected to HTTPS |
| 443 | HTTPS traffic | Everyone |
| 3306 | MySQL database | Your application only |
| 5432 | PostgreSQL database | Your application only |
| 6379 | Redis | Your application only |
These are common default ports, although actual configurations can differ.
If your database is listening on a publicly accessible interface and the firewall allows outside connections, you’ve created an unnecessary entry point.
An attacker who discovers the exposed service can investigate its configuration, identify weaknesses and attempt unauthorized access. Redis, for example, is designed to be reached by trusted clients inside a trusted network, not by the whole internet.2
The same applies to administrative dashboards, monitoring tools and internal services.
04Staging
Development And Staging Environments
Development environments are particularly interesting because they’re often built for convenience rather than security.
Developers need to test new features, troubleshoot errors and experiment with configurations. That sometimes means enabling debugging tools, detailed error reporting or temporary authentication exceptions.
These settings are useful during development, but dangerous when exposed publicly.
For example, a Laravel application accidentally deployed with APP_DEBUG=true can reveal detailed error information, including internal file paths, configuration details and potentially sensitive application data. Laravel’s own documentation says it should always be off in production.3
Other common problems include:
- Development servers accessible without authentication.
- Test accounts with predictable passwords.
- Debugging interfaces exposed publicly.
- Temporary files containing credentials.
- Database copies containing real customer information.
- Deployment tools accessible from unrestricted IP addresses.
The biggest issue is that staging environments are frequently forgotten after development is complete. A staging copy should sit behind a login and stay out of search results too, as our website build-out checklist covers.
They remain online, sometimes for years, without anyone checking whether they’re still secure.
05APIs
APIs And Forgotten Endpoints
Modern applications rely heavily on APIs.
Your customer dashboard might communicate with a Laravel backend, and your admin panel might use the same API. Your ecommerce store might connect to inventory management, CRM and shipping services.
Each integration introduces additional endpoints that need to be secured. And not every endpoint is necessarily visible through the application’s user interface.
For example, a customer might normally access an order through /api/orders/1024. But what happens if they change the number to /api/orders/1025?
GET /api/orders/1024Your order: two items, delivered TuesdayGET /api/orders/1025Another customer’s order: name, address and phone
If the application only checks whether someone is logged in, rather than verifying that they actually own the requested order, another customer’s information could become accessible.
This type of vulnerability is known as Broken Object Level Authorization (BOLA), and it sits at the top of OWASP’s list of API security risks.4
Other potential API weaknesses include:
- Missing authentication.
- Incorrect permission checks.
- Excessive information returned by API responses.
- Unrestricted requests and insufficient rate limiting.
- Old endpoints that are no longer used but remain accessible.
- API keys accidentally exposed in publicly accessible code.
06Secrets
Exposed Backups, Configuration Files And Secrets
Backups are essential. Configuration files are essential. API credentials are essential.
But none of them should be sitting in publicly accessible directories.
Imagine a website where an old database backup was accidentally uploaded into a public folder.
If directory access isn’t restricted and the file can be downloaded directly, an attacker might obtain a copy of the database without ever compromising the application’s login system.5
The same problem applies to configuration files. A publicly accessible .env file in a Laravel or PHP application could expose:
Database Logins
Database usernames and passwords.
Encryption Keys
Application encryption keys.
API Credentials
Third-party API credentials.
Email Logins
Email service credentials.
Everything Else
Other sensitive configuration values.
07Dependencies
Third-Party Plugins And Software Dependencies
Your application probably uses software written by other people.
WordPress
An installation might have dozens of plugins.
Laravel
An application might depend on numerous Composer packages.
Node.js
An application could contain hundreds of npm dependencies.
Every dependency introduces another component that needs to be maintained.
A plugin that hasn’t received updates in two years might contain a known vulnerability. An abandoned package could have security problems that will never be corrected.6
The situation becomes more complicated when a third-party component is compromised or a malicious software update introduces unwanted functionality.
Even if your own application code is well written, vulnerable dependencies can create security problems throughout the stack.
08Hosting
Misconfigured Hosting And Cloud Infrastructure
Infrastructure configuration is another major source of exposure.
A server can run perfectly well while being configured in ways that create unnecessary security risks. Examples include:
- Public cloud storage containing private files.
- Firewall rules allowing unrestricted access.
- SSH configured to permit root password logins.
- Applications running with excessive system permissions.
- Insecure file and directory permissions.
- Unnecessary services enabled by default.
- Administrative interfaces accessible from anywhere.
These problems can be particularly difficult to identify because everything appears to work normally.7
The application loads. Customers can log in. Orders are processed. Nothing looks broken.
But functionality and security are two very different things.
09Reconnaissance
How Do Hackers Discover These Hidden Entry Points?
Attackers don’t need to know your internal infrastructure to start investigating it. A surprising amount of information is publicly available.
DNS records can reveal subdomains. Digital certificates can expose additional hostnames, since every certificate a site is issued is recorded in public logs that anyone can search.8 Search engines can index forgotten pages. Public source repositories can accidentally reveal credentials or internal configuration details.
Automated scanning tools can also identify exposed services, outdated software and known vulnerabilities. A typical reconnaissance process might involve:
-
Find The Main Domains
Identifying the company’s primary domains.
-
Discover Subdomains
Discovering additional subdomains.
-
Map Servers And Services
Mapping publicly accessible servers and services.
-
Identify The Software
Identifying software versions and technologies.
-
Check For Known Flaws
Checking for known vulnerabilities.
-
Probe Admin Panels And APIs
Investigating exposed administrative interfaces and APIs.
-
Pick The Easiest Way In
Prioritizing potential entry points for further testing.
None of this necessarily requires compromising the main website.
In fact, an attacker might find an easier route through an older application that nobody has touched in years.
This is why checking only your primary domain provides an incomplete picture of your security.
10Reduce It
How To Reduce Your Attack Surface
You don’t necessarily need to rebuild your infrastructure or purchase expensive enterprise security software.
In many cases, reducing your attack surface starts with understanding what you already have.9
Here are several practical steps worth taking.
| Security Measure | What It Accomplishes |
|---|---|
| Maintain an asset inventory | Identifies every server, domain, application and service |
| Remove unused subdomains | Retires forgotten applications and unnecessary exposure |
| Restrict network access | Keeps databases and internal services away from public connections |
| Secure development environments | Prevents testing tools and debug interfaces from becoming entry points |
| Review API permissions | Restricts access to authorized users and resources |
| Protect configuration files | Keeps credentials, backups and secrets out of public directories |
| Update dependencies | Addresses known vulnerabilities in third-party software |
| Harden server configurations | Reduces unnecessary services and excessive permissions |
| Monitor exposed assets | Identifies changes and newly introduced entry points |
One particularly important point: This isn’t a one-time exercise.
Applications change constantly. New features introduce endpoints, developers create temporary environments, software dependencies receive updates and infrastructure gets reconfigured.
Your attack surface today might look very different six months from now.
11Regular Reviews
Why Regular Security Reviews Matter
Even a well-maintained application can develop security weaknesses over time.
A new integration might introduce an exposed API. A developer might accidentally leave a testing environment accessible. An update could introduce a configuration change that exposes an internal service.
And these changes don’t always trigger obvious errors.
That’s why we approach security as an ongoing process rather than a checklist completed once during development.
At Clickative, we look beyond the primary website. Our security reviews examine the infrastructure supporting your application, including hosting configuration, software versions, exposed services, authentication, permissions, dependencies and publicly accessible files.
We also look at how the different components interact. For example, a database might be properly protected from direct internet access, but an API endpoint could still expose sensitive database records because of missing authorization checks.
Infrastructure ReviewServers, hosting and services
Application TestingLogins, permissions and APIs
BothLooking at individual components in isolation won’t necessarily reveal problems that exist between them.
We combine infrastructure reviews with application-level testing to identify weaknesses, explain their impact and establish what needs to be addressed first.
For businesses requiring ongoing security testing, our red teaming service goes further by testing the application, its APIs, authentication systems and exposed infrastructure through controlled attack campaigns.
And importantly, we don’t simply hand over a list of problems and leave you to figure everything out. We can work through the fixes ourselves or provide clear recommendations for your existing development team.
Every assessment starts with a written scope that you approve before testing begins.
12The Whole Picture
Your Website Is Only One Piece Of The Puzzle
The biggest mistake businesses make is assuming that a secure-looking website means their entire infrastructure is secure.
Your homepage might be perfectly configured while an old staging server exposes outdated software. Your login system might be protected by two-factor authentication while an administrative API has missing permission checks.
Security needs to account for the entire environment, not just the parts customers can see.
The first step is knowing exactly what’s exposed.
At Clickative, we help solo builders, SaaS teams, ecommerce businesses and small companies identify vulnerabilities across their applications and infrastructure, fix the problems and keep watch for new threats.
Not Sure What’s Running Under Your Application?
Our Security Review examines your server, hosting, frameworks, dependencies, access controls and exposed files, then provides a prioritized report explaining what we found and what to fix first.
You don’t need an enterprise security department to take your application’s security seriously.
Every assessment starts with a written scope that you approve before testing begins.
References
- OWASP Web Security Testing Guide: Test for subdomain takeover
- Redis: Security
- Laravel: Configuration, debug mode
- OWASP API Security Top 10: API1:2023 Broken Object Level Authorization
- OWASP Web Security Testing Guide: Review old backup and unreferenced files
- OWASP Top 10: Vulnerable and outdated components
- OWASP Top 10: Security misconfiguration and Amazon S3: Blocking public access
- Certificate Transparency: How it works
- CIS Critical Security Controls: Inventory and control of enterprise assets